Blog
AI Security
AI is changing both what we build and how fast attackers move. This collection explores threat modeling for AI and LLM systems, AI supply chain risk, agentic workflows and protocols like MCP, and how security teams can keep design reviews ahead of AI-driven development. Practical analysis for teams securing AI in production.
Latest articles
Blog
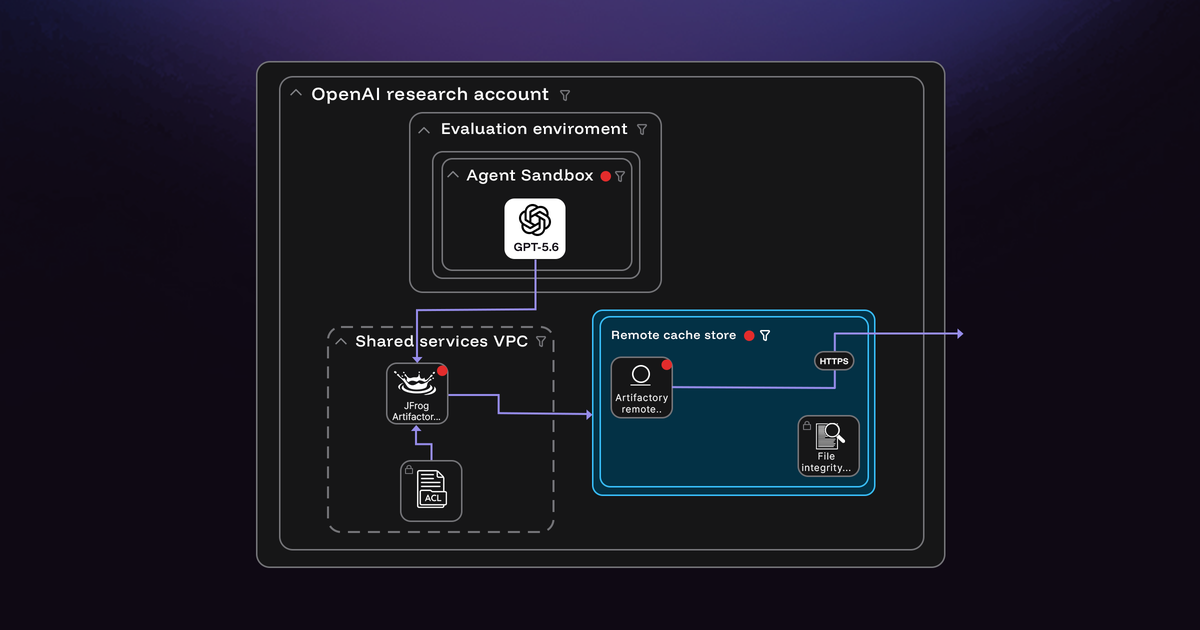
Beyond the sandbox: Threat modeling the OpenAI and Hugging Face incident
We explored the initial sandbox escape in the OpenAI and Hugging Face incident. Here’s what it reveals about trust boundaries, connected services, and secure design in an agentic era.

Blog
Secure by Design: Proactive Resilience in the era of AI Supply Chain Risk and MCP
After an MCP vulnerability reportedly impacting over 150 million downloads, see why AI supply chain risk demands architectural threat modeling, not just reactive scanning.


A simple starting point
Ready to see threat modeling in practice?
Walk through what continuous, architecture-aware threat modeling looks like for your environment.
