Blog
Browse expert guides on threat modeling, CMS security, content strategy, and more. Essential resources for security professionals and developers.
All Blog Posts
Showing all posts
Blog
Trike Threat Modeling Methodology
Trike is an open-source, risk-based threat modeling methodology built on a requirements model and a data flow diagram. See how it works, plus pros and cons.
trike-threat-modeling-methodology
Blog
PASTA Threat Modeling Methodology
PASTA is a risk-centric, 7-step threat modeling methodology that ties technical risk to business impact and compliance.
pasta-threat-modeling-methodology
Blog
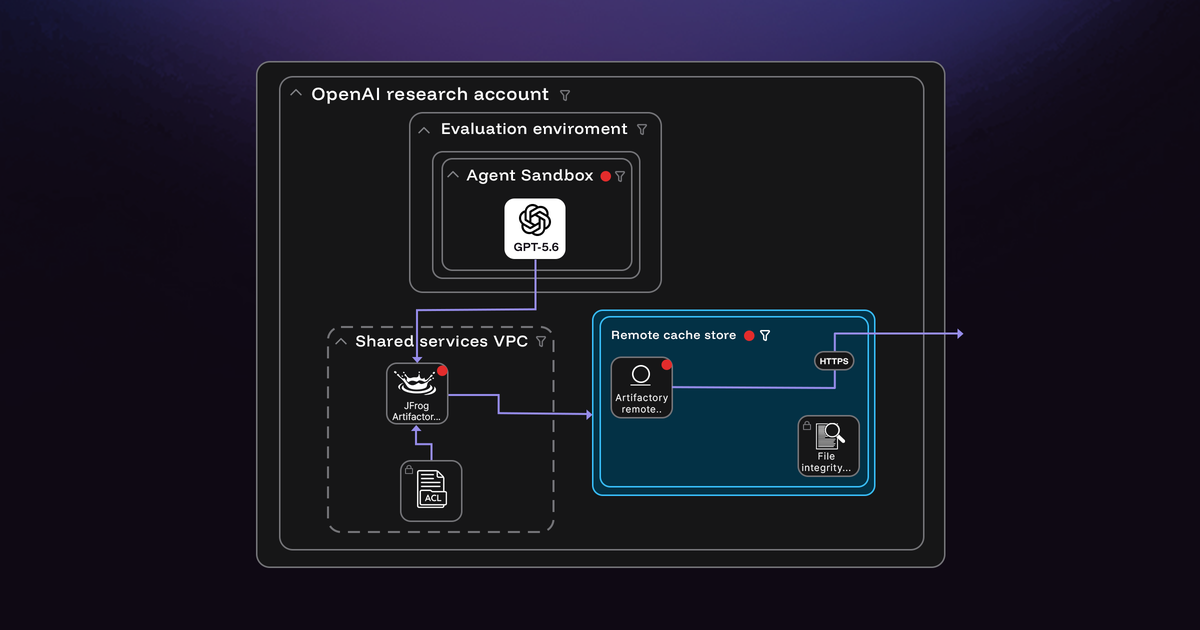
Beyond the sandbox: Threat modeling the OpenAI and Hugging Face incident
We explored the initial sandbox escape in the OpenAI and Hugging Face incident. Here’s what it reveals about trust boundaries, connected services, and secure design in an agentic era.
beyond-the-sandbox-threat-modeling-the-openai-and-hugging-face-incident
Blog
OCTAVE Threat Modeling Methodology
OCTAVE threat modeling is a risk assessment methodology for organizational cybersecurity risk. See how OCTAVE, OCTAVE-S, OCTAVE Allegro, and OCTAVE FORTE work.
octave-threat-modeling-methodology
Blog
ThreatModeler Achieves FedRAMP Moderate Authorization
Bringing continuous, automated threat modeling to federal agencies without slowing down the mission.
threatmodeler-achieves-fedramp-moderate-authorization
Blog
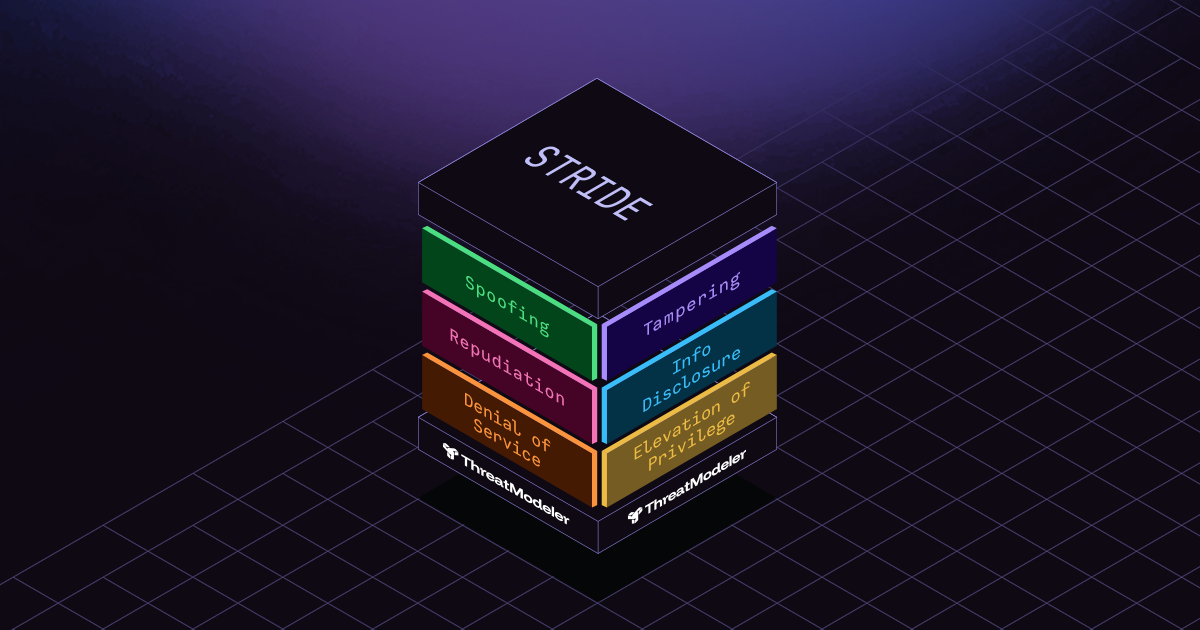
STRIDE Threat Modeling Methodology Explained (2026)
What is STRIDE threat modeling? Learn the six threat categories, real benefits and limitations, and how to apply STRIDE in 2026.
stride-threat-modeling-methodology

Blog
Secure by Design: Proactive Resilience in the era of AI Supply Chain Risk and MCP
After an MCP vulnerability reportedly impacting over 150 million downloads, see why AI supply chain risk demands architectural threat modeling, not just reactive scanning.
secure-by-design-proactive-resilience-in-the-era-of-ai-supply-chain-risk-and-mcp

Blog
Calm in the Chaos: Why Threat Modeling Matters More as AI Speeds Up the Build-Exploit-Patch Cycle
As AI accelerates the build-exploit-patch cycle, see why threat modeling — not more scanning — is the discipline built for this moment.
calm-in-the-chaos-why-threat-modeling-matters-more-as-ai-speeds-up-the-build-exploit-patch-cycle

Blog
When GPS Assumptions Fail: Lessons for Threat Modeling
A new advisory on GPS spoofing is a wake-up call — see why so many systems still run on trust assumptions that no longer hold up.
when-gps-assumptions-fail-lessons-for-threat-modeling
Blog
2026 Predictions: AI-Acceleration Will Shift Security Back to Design
With global cybercrime costs projected to hit $11.3 trillion in 2026, our predictions show why secure-by-design is becoming a business requirement, not a buzzword.
2026-predictions-ai-acceleration-will-shift-security-back-to-design

Blog
Why Healthcare M&A Requires Threat Modeling: Before the Deal Closes
Healthcare M&A deals inherit far more than revenue — see why threat modeling needs to be a non-negotiable part of due diligence, not an afterthought.
why-healthcare-ma-requires-threat-modeling-before-the-deal-closes

Blog
Start Left At Design: Lessons From a CISO Panel
A CISO panel reveals why most "shift left" efforts still fail — and why real progress starts with design review, not later-stage scanning.
start-left-at-design-lessons-from-a-ciso-panel

Blog
Securing Cloud Infrastructure at Scale with ThreatModeler and HashiCorp
See how ThreatModeler's partnership with HashiCorp pairs Terraform automation with intelligent threat modeling to build secure-by-design cloud infrastructure at scale.
securing-cloud-infrastructure-at-scale-with-threatmodeler-and-hashicorp
Blog
Why Threat Modeling Your Third-Party Integrations Should Be Standard Practice
A weak admin password exposed candidate data on McDonald's AI hiring platform — a reminder that vendor integrations deserve the same threat modeling rigor as your own systems.
why-threat-modeling-your-third-party-integrations-should-be-standard-practice
Blog
Modern Threat Modeling for Financial Services: Cybersecurity and Compliance at Scale
With financial-sector breaches averaging $5.9 million, see how modern threat modeling helps banks and fintechs close the visibility gaps manual processes can't scale to cover.
modern-threat-modeling-for-financial-services-cybersecurity-and-compliance-at-scale
No posts in this category yet.
beyond-the-sandbox-threat-modeling-the-openai-and-hugging-face-incident
2026-predictions-ai-acceleration-will-shift-security-back-to-design
calm-in-the-chaos-why-threat-modeling-matters-more-as-ai-speeds-up-the-build-exploit-patch-cycle
secure-by-design-proactive-resilience-in-the-era-of-ai-supply-chain-risk-and-mcp
stride-threat-modeling-methodology
when-gps-assumptions-fail-lessons-for-threat-modeling
calm-in-the-chaos-why-threat-modeling-matters-more-as-ai-speeds-up-the-build-exploit-patch-cycle
trike-threat-modeling-methodology
pasta-threat-modeling-methodology
octave-threat-modeling-methodology
stride-threat-modeling-methodology
beyond-the-sandbox-threat-modeling-the-openai-and-hugging-face-incident
the-threat-modeling-tools-market-is-booming-heres-what-you-should-know
start-left-at-design-lessons-from-a-ciso-panel
2026-predictions-ai-acceleration-will-shift-security-back-to-design
secure-by-design-proactive-resilience-in-the-era-of-ai-supply-chain-risk-and-mcp
why-threat-modeling-your-third-party-integrations-should-be-standard-practice
securing-cloud-infrastructure-at-scale-with-threatmodeler-and-hashicorp
when-gps-assumptions-fail-lessons-for-threat-modeling
securing-cloud-infrastructure-at-scale-with-threatmodeler-and-hashicorp
the-threat-modeling-tools-market-is-booming-heres-what-you-should-know
modern-threat-modeling-for-financial-services-cybersecurity-and-compliance-at-scale
trike-threat-modeling-methodology
pasta-threat-modeling-methodology
octave-threat-modeling-methodology
threatmodeler-achieves-fedramp-moderate-authorization
why-threat-modeling-your-third-party-integrations-should-be-standard-practice
start-left-at-design-lessons-from-a-ciso-panel
why-healthcare-ma-requires-threat-modeling-before-the-deal-closes
modern-threat-modeling-for-financial-services-cybersecurity-and-compliance-at-scale
threatmodeler-achieves-fedramp-moderate-authorization
A simple starting point
Ready to see threat modeling in practice?
Walk through what continuous, architecture-aware threat modeling looks like for your environment.
