Blog
Secure by Design & DevSecOps
Security is cheapest and most effective when it starts at design. These articles cover Secure by Design principles, shift-left practices and how to bring threat modeling into DevSecOps workflows without slowing delivery. Read perspectives from CISOs, security architects and engineering leaders on making secure design a repeatable habit.
Latest articles
Blog
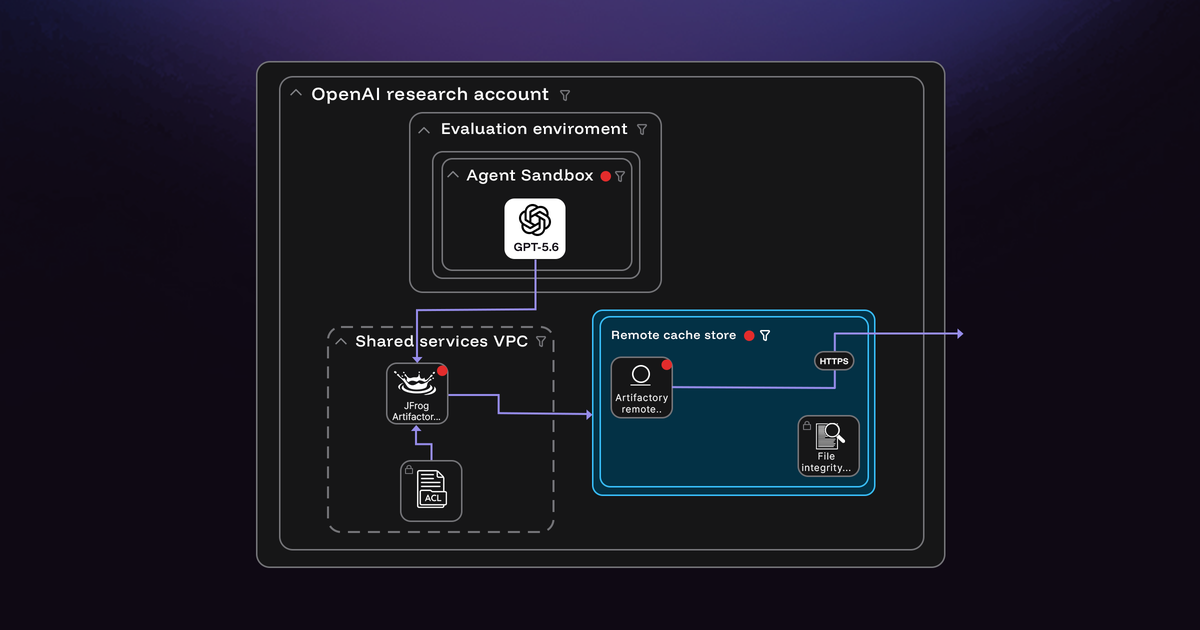
Beyond the sandbox: Threat modeling the OpenAI and Hugging Face incident
We explored the initial sandbox escape in the OpenAI and Hugging Face incident. Here’s what it reveals about trust boundaries, connected services, and secure design in an agentic era.

Blog
Secure by Design: Proactive Resilience in the era of AI Supply Chain Risk and MCP
After an MCP vulnerability reportedly impacting over 150 million downloads, see why AI supply chain risk demands architectural threat modeling, not just reactive scanning.

Blog
2026 Predictions: AI-Acceleration Will Shift Security Back to Design
With global cybercrime costs projected to hit $11.3 trillion in 2026, our predictions show why secure-by-design is becoming a business requirement, not a buzzword.


A simple starting point
Ready to see threat modeling in practice?
Walk through what continuous, architecture-aware threat modeling looks like for your environment.
